DPDP, a module of PII Discovery
Breach Register
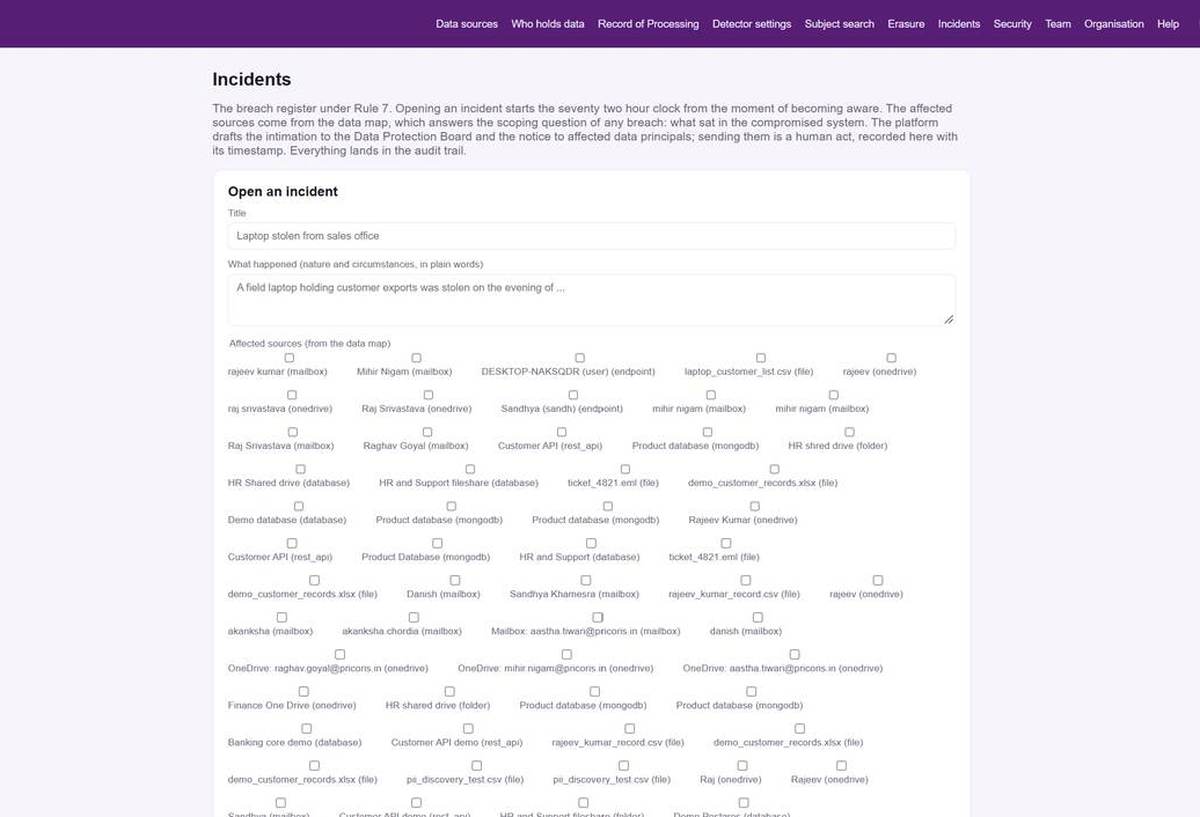
Two clocks, one data map. Opening an incident starts the CERT-In and the DPDP timelines, the affected data comes from what discovery actually found, and the intimation to the Data Protection Board and the notices to affected people are drafted, sent and recorded.
What it does
- Opens an incident with the time of becoming aware and starts two clocks: six hours to CERT-In under the 2022 directions, seventy two hours to the Data Protection Board under Rule 7.
- Scopes the breach from the data map: affected sources are ticked from what discovery found, and the affected data principals follow from the sources, not from a guess.
- Drafts the intimation to the Board and the notice to affected data principals from the incident record; sending is a human act, recorded with its timestamp.
- Routes the principal notices through Consent and Rights, so every letter to every person is composed, sent and recorded whether or not it arrived, in the person's language.
- Containment log with actions, assignee, deadline and evidence attachments; a closure step; a regulator ready incident report export.
- Opens an incident from a SIEM alert by API; every step lands in the audit trail.
How it maps to the law
| Obligation | Where | What the product does | Status |
|---|---|---|---|
| Intimate the Board and affected data principals | Section 8(6), Rule 7 | Incident register with the 72 hour clock, drafted intimation and notices. | Built |
| Report cyber incidents to CERT-In | CERT-In directions 2022 | Six hour clock alongside, on the same incident. | In build, September 2026 |
| Know what sat in the compromised system | Section 8(1) | Affected sources and principals from the data map. | Built |
| Notify each affected person | Rule 7(1) | Bulk notices through Consent and Rights, recorded per person. | In build, September 2026 |
| Keep the record of what was done | Rule 7(2) | Containment log, evidence attachments, closure, audit trail. | In build, September 2026 |
Honest limits
- The register does not detect breaches; it manages them. Detection stays with your security tooling, which can open an incident here by API.
- Notifications to regulators other than the Board and CERT-In are drafted by template only when a customer needs them.
Licensing
The Breach Register is licensed on its own, without the full discovery seat count, for organisations that want the register and the clocks first and discovery later.
Run a tabletop on the register
Open a stolen laptop incident in the demo, scope it from the data map, and draft the intimation. Forty minutes.