Proof, not paperwork.
Software for two subjects that now land on the same desk: personal data protection under the DPDP Act, and the governance of AI systems under ISO 42001 and the EU AI Act. In both, the operational tools do the work and the GRC system is filled by what they did. The GRC is filled by the tools, not by uploads.
DPDP
Four operational tools and one GRC system. PII Discovery finds the data, Consent and Rights takes consent on it and answers the person, Cookie Consent governs the website and the app, the Breach Register scopes an incident from the data map, and PIMS GRC on ISO 27701 holds the controls and the evidence the tools wrote.
AI Governance
One operational tool and one GRC system. SPRICO tests the deployed AI system; AISIA governs it on ISO 42001, NIST AI RMF and the EU AI Act, and the test results land as control evidence.
Who each edition is for
DPDP Starter: startups, MSMEs and D2C brands. Hosted, fixed annual price, set up in an afternoon: consent and rights, cookie consent, breach register, notice templates.
DPDP Enterprise: banks, hospitals, insurers, telecom and education groups. Self hosted, sector packs, SSO, PII Discovery, PIMS GRC, implementation by Pricoris LLP.
AI Startup: AI companies asked for ISO 42001 evidence and red team results in a customer's due diligence.
AI Enterprise: organisations adopting AI, with the vendor register for the AI tools they buy.
Built for how Indian data looks
Aadhaar with the Verhoeff checksum, PAN, ABHA, UHID, UPI, IFSC, APAAR, GSTIN and card numbers checked by Luhn are recognised in the engine, not bolted on. Notices and consent run in English and the scheduled languages. Guardian verification follows the routes the Rules recognise. Six sector policy packs know what a hospital page, a net banking session or a student portal may and may not share.
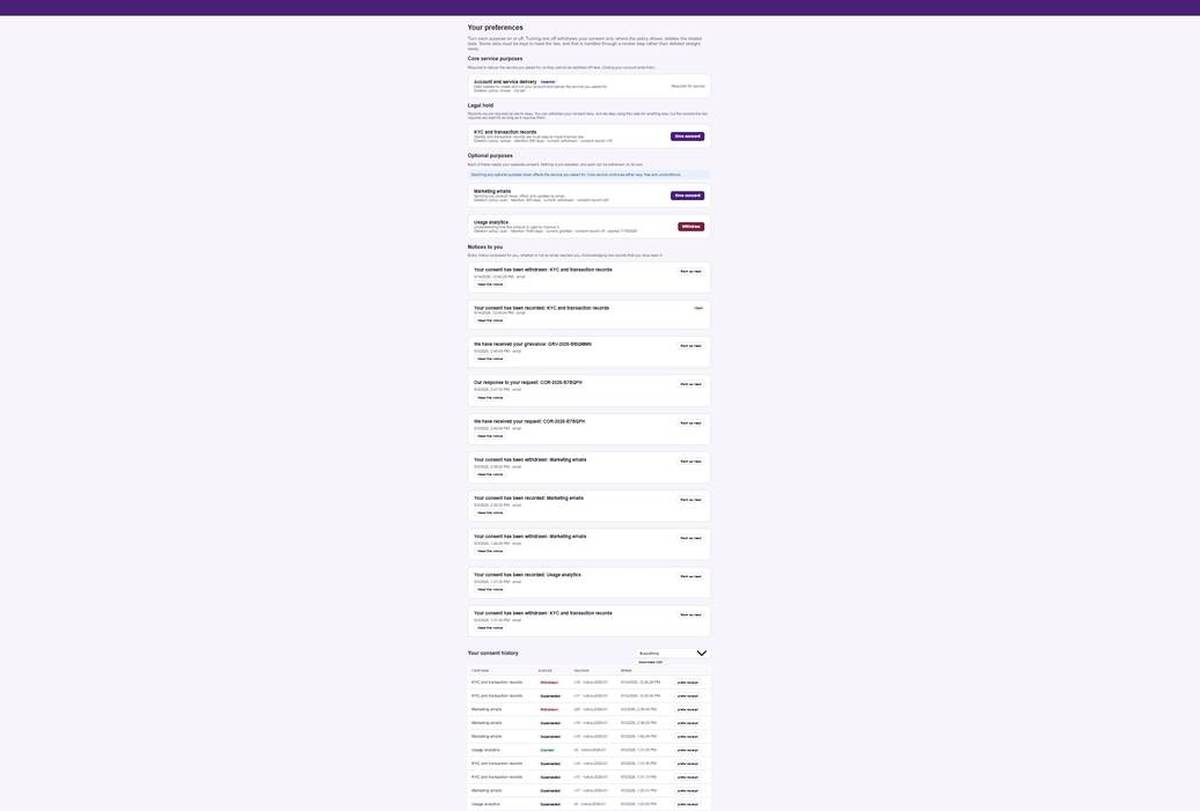
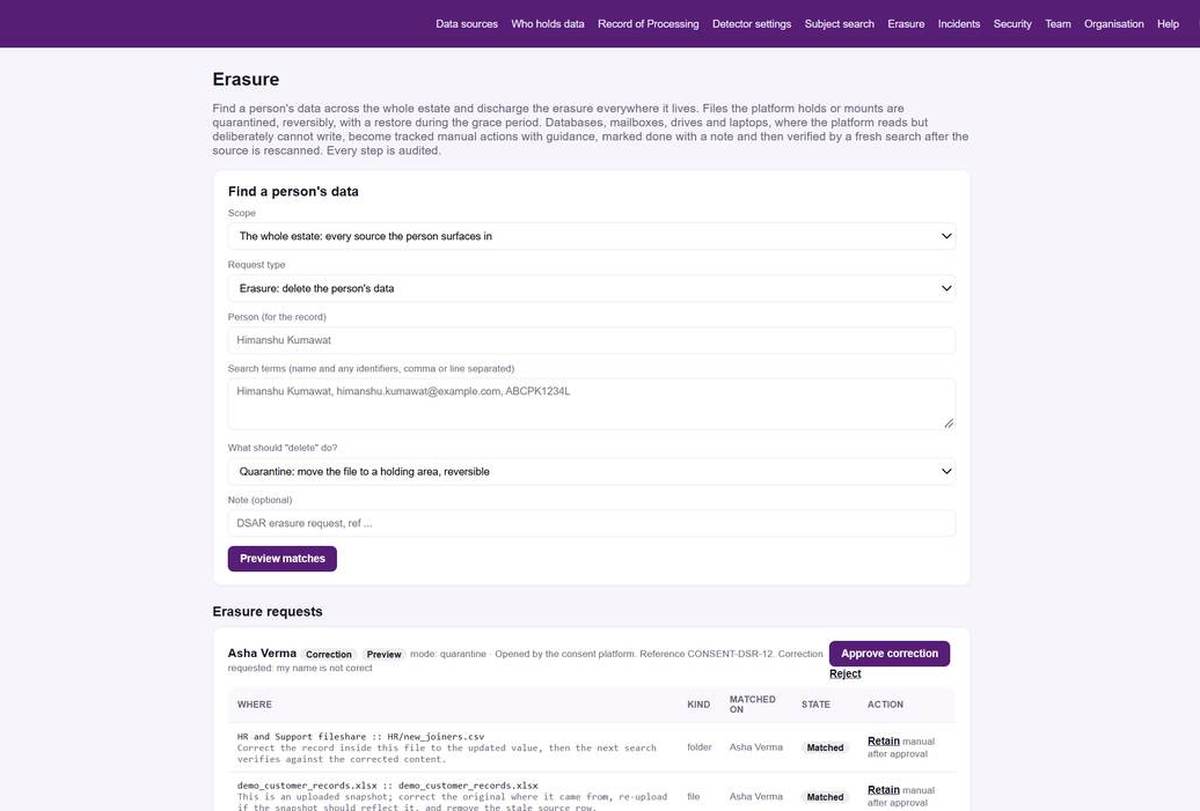
What "proof" looks like
Sectors the products already understand
Healthcare, banking and finance, insurance, education, ecommerce, telecom, travel. The identifiers, the sensitive journeys and the retention classes of each are in the detectors, the policy packs and the sector presets.
Honest limits, on every page
Each product page states what the product does not yet do. A compliance buyer finds the gaps anyway; we would rather you found them here.
See it on your own data
A demo runs on your files, your database or your website, not on a slide deck. Thirty minutes, with the operator console open.